Secure Windows Remote Administration Using a Bastion Host
Project Overview
This project focused on designing and configuring a controlled and security-focused remote administration environment for Windows systems using a Windows Bastion Host.
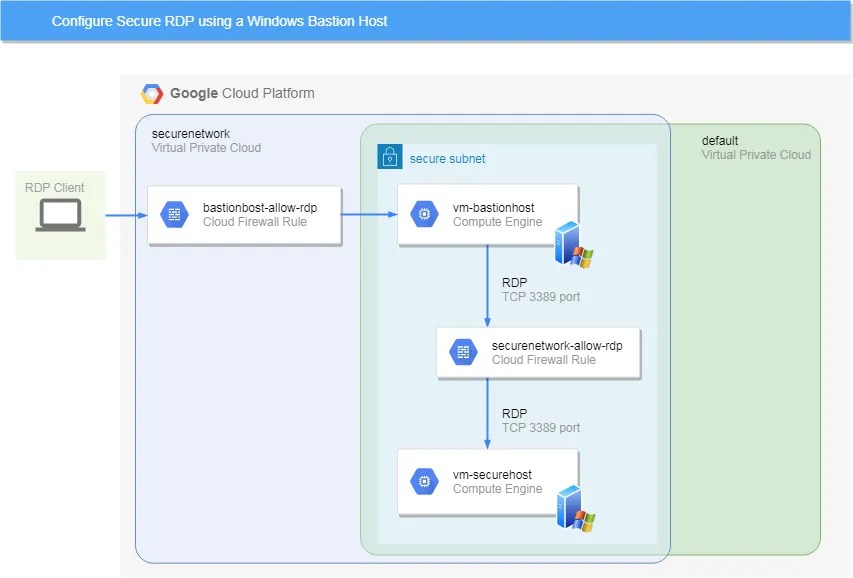
Instead of allowing administrators to connect directly to internal Windows systems through Remote Desktop Protocol (RDP), the Bastion Host acts as a controlled entry point between remote administrators and protected internal resources.
The solution was designed around network segmentation, restricted access, authentication controls, firewall policies, least-privilege principles, and security monitoring.
🏗️ Architecture
Administrator → Bastion Host → Protected Windows Systems
The Bastion Host is positioned within a dedicated management network or DMZ, providing a controlled gateway for remote administration.
This architecture helps reduce unnecessary exposure of internal systems and provides a centralized point where remote-access security policies can be applied.
🛡️ Key Security Controls
🔑 Network Level Authentication (NLA)
🔒 Restricted RDP access
🧱 Windows Defender Firewall configuration
🌐 Network segmentation
🖥️ Dedicated Bastion Host
👤 Least-privilege access
📋 Group Policy configuration
🛡️ Windows security hardening
📊 Event logging and monitoring
⚙️ PowerShell administration
💻 Technologies & Tools
🖥️ Operating Systems
Windows Server 2022
Windows 10
Windows 11
🔗 Remote Access
Remote Desktop Protocol (RDP)
Remote Desktop Connection (MSTSC)
🔐 Security & Administration
Windows Defender Firewall
Group Policy
Network Level Authentication
PowerShell
🌐 Networking
DMZ / Management Network
Network Segmentation
Access Control
📊 Monitoring & Logging
Windows Event Viewer
Windows Security Logs
🎯 Project Objectives
The primary objectives of the project were to:
Reduce the attack surface associated with remote desktop access
Prevent direct RDP exposure of protected internal systems
Establish a controlled remote administration pathway
Apply least-privilege access principles
Strengthen authentication requirements
Restrict network access through firewall rules
Improve visibility through logging and monitoring
Demonstrate secure Windows remote administration practices
⚙️ Implementation
The project involved configuring a Windows Server to function as a Bastion Host and establishing controlled remote access to protected Windows systems.
Security controls were applied at multiple layers: